Uncovering Access Pattern Discrepancies in Legacy Device Service Logs Across Multi-Site Operations
Written by Bianca Russell · May 27, 2026
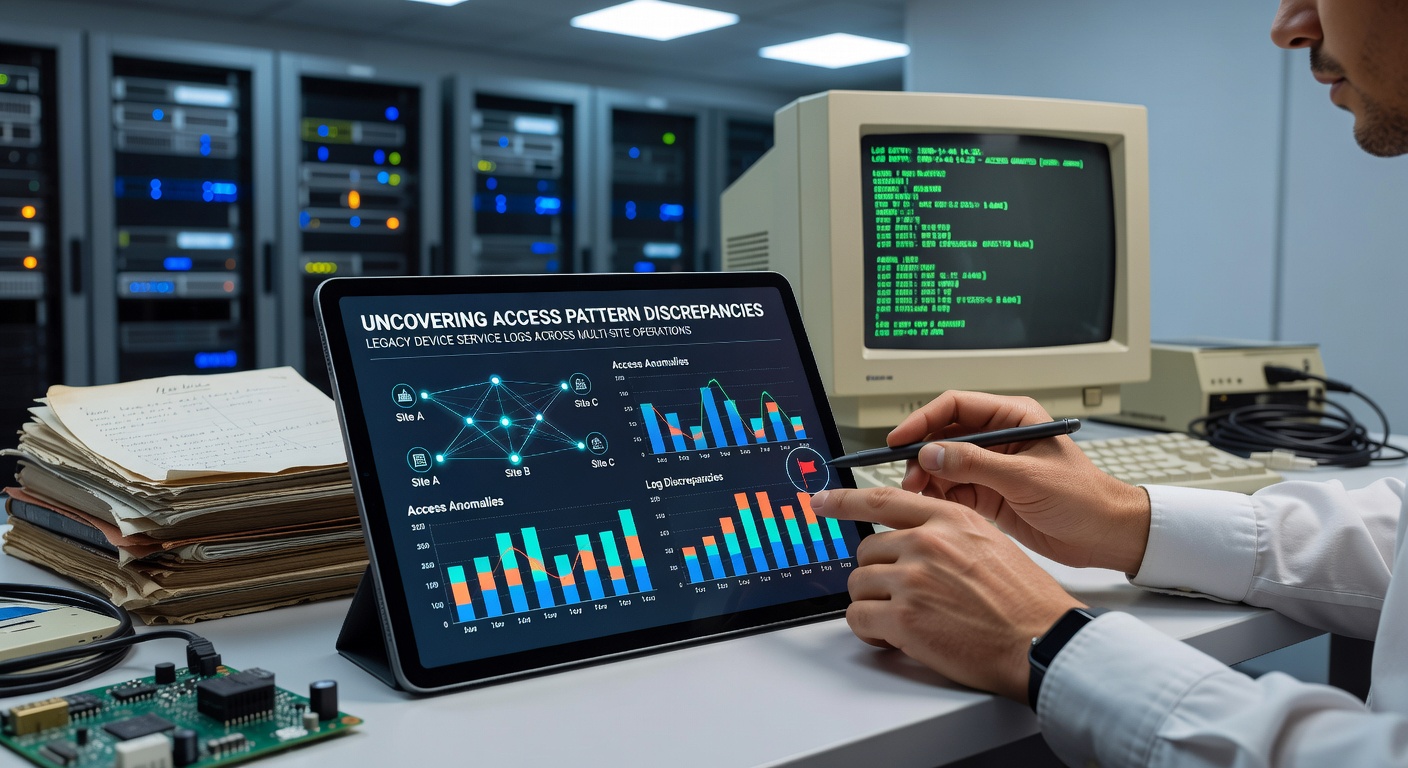
Uncovering Access Pattern Discrepancies in Legacy Device Service Logs Across Multi-Site Operations
Service logs from legacy devices often hold the key to identifying access pattern discrepancies that surface during multi-site operations, and researchers continue to develop systematic approaches for extracting these insights. Organizations managing distributed networks of older equipment face ongoing challenges when attempting to align activity records across locations that use different hardware generations and logging formats. Data indicates that inconsistencies in timestamp formats, user authentication entries, and command sequences frequently point to configuration drift or unauthorized procedural variations.
Legacy Systems and Their Logging Limitations
Legacy devices in sectors ranging from manufacturing to hospitality typically operate with embedded logging mechanisms that were designed decades ago, and these systems rarely incorporate standardized protocols for cross-site synchronization. Observers note that entries may record events in local time zones without offsets, omit user identifiers, or truncate command histories when storage buffers reach capacity. Such limitations create gaps that complicate efforts to establish baseline access patterns, particularly when sites operate under varying maintenance schedules and staff protocols.
Studies conducted by institutions like the National Institute of Standards and Technology have examined how inconsistent log structures affect anomaly detection, and findings show that even minor formatting differences can obscure repeated access sequences across facilities. Technicians working with these systems often rely on custom parsing scripts to normalize data before comparative analysis begins, yet the process remains labor-intensive when dealing with thousands of entries per site.
Methods for Detecting Pattern Discrepancies
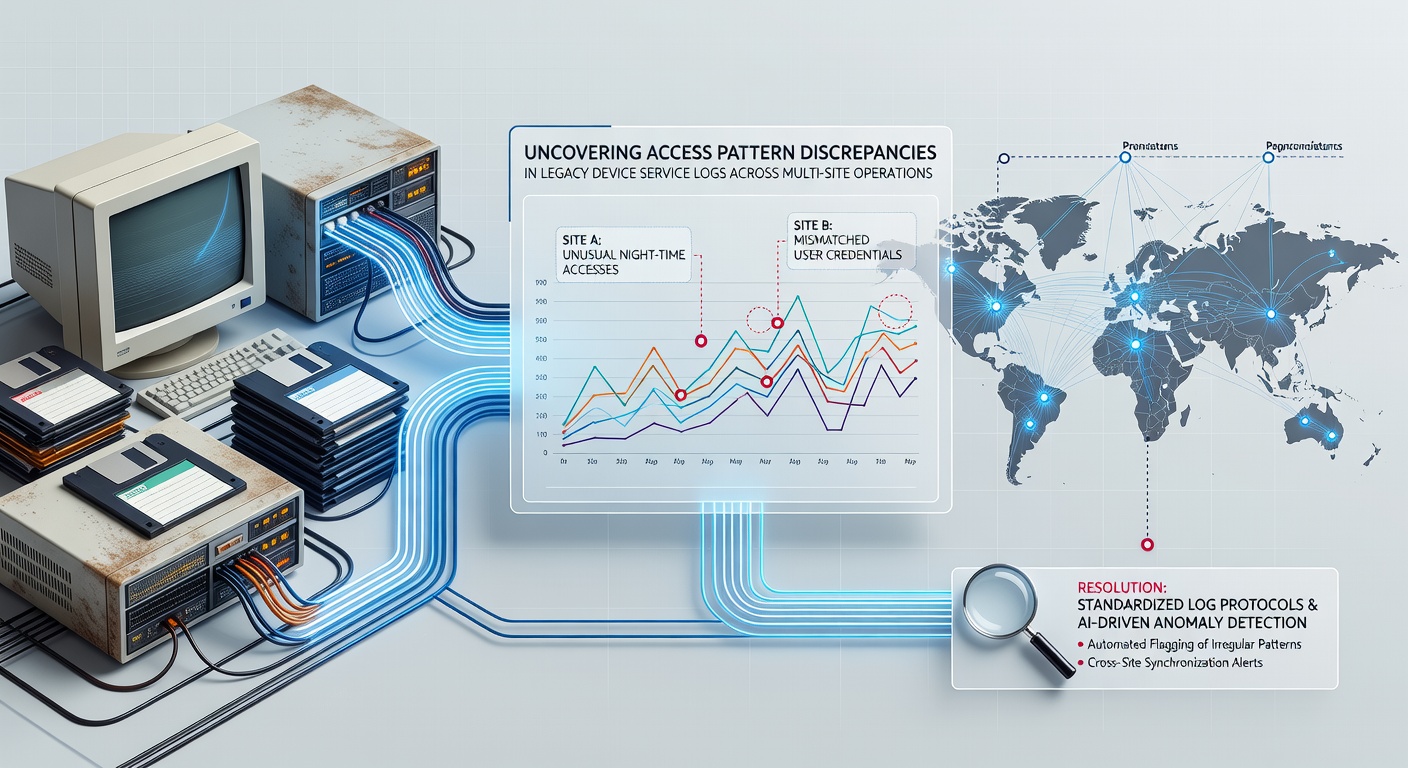
Analysts apply sequence mining algorithms and statistical clustering techniques to service logs, and these approaches help surface deviations that manual review might miss. For instance, one study revealed that access frequency spikes at certain hours aligned with shift changes at some locations but deviated sharply at others, prompting further investigation into staffing procedures. Correlation engines then compare these patterns against expected operational baselines derived from aggregated historical data.
Researchers have observed that combining log data with metadata such as device firmware versions and network connectivity status strengthens discrepancy identification. When a legacy unit at one site shows repeated service calls during periods when similar units at other sites remain idle, the variance may reflect differences in environmental conditions or undocumented configuration changes. Automated tools now flag these instances for human review while preserving chain-of-custody records for audit purposes.
Case Examples from Multi-Site Environments
Take one regional healthcare network that discovered access pattern mismatches in its legacy patient monitoring equipment across five campuses, and investigators traced the discrepancies to differing vendor support contracts that altered remote diagnostic permissions. Data from May 2026 indicated that similar issues emerged in transportation logistics operations where older vehicle diagnostic units logged maintenance access at irregular intervals depending on regional depot policies. These examples illustrate how cross-referencing logs reveals procedural inconsistencies without requiring hardware replacement.
Industry reports from organizations such as the IEEE Standards Association emphasize the value of establishing centralized log repositories that ingest data from legacy sources through protocol converters. Once normalized, the aggregated dataset supports machine learning models trained to recognize normal versus anomalous access sequences across geographic boundaries. Implementation timelines vary, yet organizations report measurable improvements in identifying configuration drift within six months of deployment.
Integration with Modern Monitoring Frameworks
Modern security information and event management platforms increasingly incorporate connectors for legacy log formats, and this integration allows real-time comparison of access events across sites. When discrepancies appear, such as unexpected privilege escalations at one location, automated alerts route to operations teams equipped with standardized response playbooks. Evidence suggests that early detection of these variances reduces downtime associated with inconsistent maintenance practices.
Academic work published through European research consortia has explored graph-based representations of log entries, where nodes represent users or devices and edges capture temporal relationships. This modeling approach highlights clusters of activity that deviate from the network-wide norm, providing visual cues that accelerate root-cause analysis. Operators in multi-site retail environments have applied similar techniques to point-of-sale terminals still running older operating systems.
Future Directions and Standardization Efforts
Ongoing initiatives aim to define minimum logging requirements for legacy device interfaces, and participation from manufacturers across North America, Europe, and Asia-Pacific regions supports broader adoption. Standards bodies continue to refine guidelines that address timestamp precision, authentication granularity, and retention periods, all of which directly influence the reliability of cross-site pattern analysis. As more facilities migrate portions of their infrastructure, hybrid logging environments will likely persist, sustaining the need for robust discrepancy detection methods.
Conclusion
Effective uncovering of access pattern discrepancies in legacy device service logs requires consistent data normalization, algorithmic comparison, and integration with contemporary monitoring tools, and organizations that implement these practices gain clearer visibility into multi-site operational variances. Continued refinement of standards and analytical techniques supports more reliable identification of inconsistencies that affect performance and compliance across distributed environments.